ENVELOPE ENCRYPTION
Per-Record AES-256-GCM
Every single entry is encrypted with its own uniquely generated 96-bit initialization vector. A compromise of one record gives zero insight into any other record in your vault.
Voltrex Vault is a zero-knowledge desktop password and secrets manager. Powered by local AES-256-GCM envelope encryption, hardened Argon2id key derivation, and an embedded SQLite database. No mandatory cloud accounts. No telemetry.
 VOLTREX VAULT v1.0
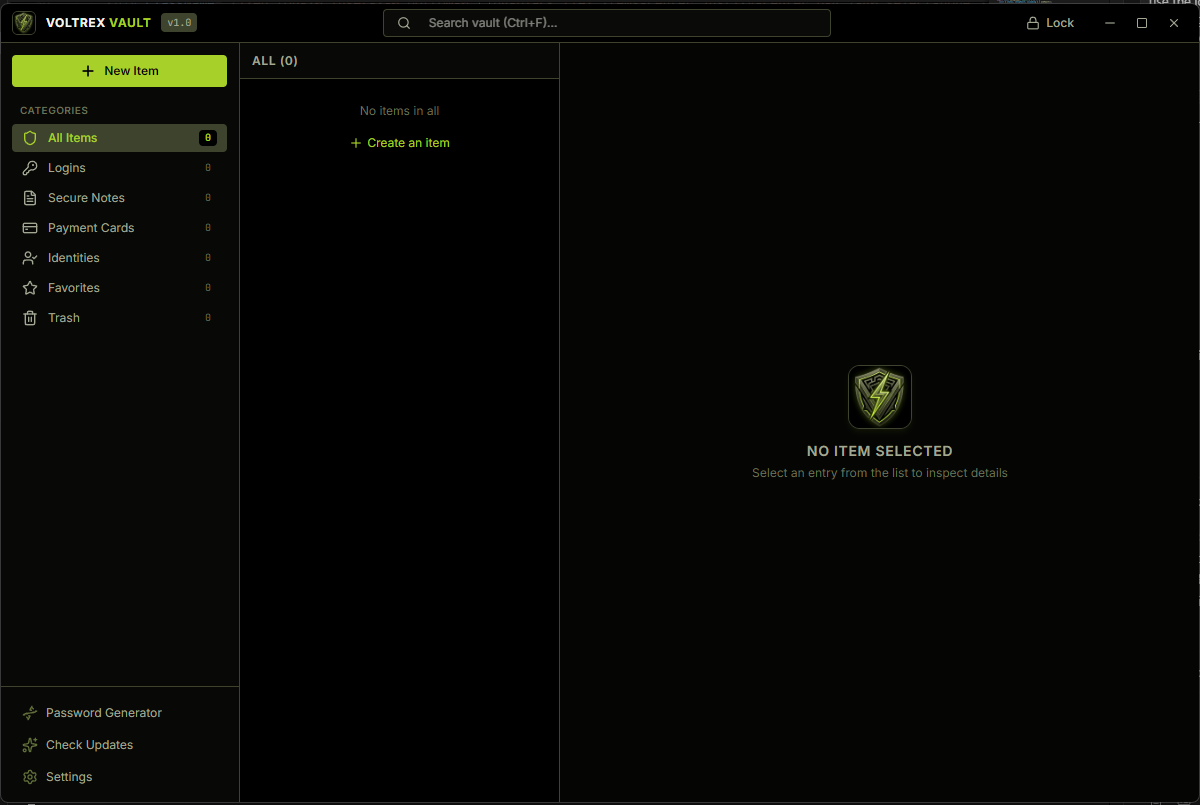
0600 permissions.connect-src 'none'.An ergonomic, dark-mode interface built with high-contrast typography, keyboard shortcuts, and zero distracting visual noise.
Essential credential management tools designed to keep you in control of your data without third-party subscriptions.
Every single entry is encrypted with its own uniquely generated 96-bit initialization vector. A compromise of one record gives zero insight into any other record in your vault.
Migrate seamlessly. Built-in parser extracts credentials from Bitwarden, Google Chrome, 1Password, and LastPass CSV exports, including multi-line notes and 2FA secrets.
Generate non-predictable passwords with real-time Shannon entropy calculation (up to 128+ bits). Tailor character sets and filter visually ambiguous glyphs like 0/O/l/1.
Export standalone .voltrex containers encrypted with master-password-derived keys. Supports atomic rollback snapshots and cross-vault collision detection.
Automatic inactivity locks engage when user interaction stops. Copied passwords are automatically purged from the operating system clipboard after 15 to 120 seconds.
Voltrex Vault has no telemetry, no tracking analytics, and no remote dependencies. It functions perfectly inside completely air-gapped environments.
How Voltrex Vault protects your credentials against physical theft, memory snooping, and tampering.
Provided by user. Never persisted to disk in any form.
64 MiB RAM, 3 iterations, 32-byte salt → derives 256-bit KEK.
KEK decrypts the Vault Data Encryption Key (DEK) via AES-256-GCM.
Individual records decrypted on demand. Zeroized on lock.
| Attack Vector | Security Guarantee | Mitigation Technique |
|---|---|---|
| Database Stolen at Rest | Zero Plaintext Exposure | All payload blobs stored as AES-256-GCM ciphertext in SQLite with 0600 filesystem mode. |
| Ciphertext Tampering | Cryptographic Rejection | 128-bit authentication tag checked prior to decryption. Any altered bit raises CryptoIntegrityError. |
| Memory Snooping | Ephemeral Key Lifetime | Key buffers (DEK, KEK) are zeroized immediately with buf.fill(0) upon vault locking or app shutdown. |
| IPC Spoofing / XSS | Strict Boundary Isolation | Electron contextIsolation: true, strict CSP (connect-src 'none'), senderFrame validation. |
| Data Corruption on Restore | Pre-Restore Rollback | Automatic point-in-time SQLite snapshot created before executing any container restore operations. |
Binaries are packaged with automated SHA-256 blockmaps and signed executables.
Standard NSIS Setup with desktop shortcut and automated uninstaller.
Portable Linux binary archive. Extract and run on any modern Linux distribution.
Single executable for Linux with zero dependencies. Run directly after chmod +x.
# Clone the repository
git clone https://github.com/ziard47/voltrex-vault.git
cd voltrex-vault

# Install dependencies
npm install

# Run all 44 automated cryptographic and security tests
npm test

# Launch the desktop application
npm startInspect the underlying security proofs and system architecture files directly in this repository.
Comprehensive breakdown of IPC isolation, SQLite repository schema, key unwrap lifecycles, and memory zeroization.
Formal analysis of adversary capabilities, offline attacks, memory dumping mitigations, and cross-site scripting prevention.